
Point-of-sale systems sit at the intersection of payments, customer data, store operations, and technology infrastructure, making vendor reliability increasingly important for retailers. A 2026 Global Third-Party Risk Management Survey found that cyber risk is the second-largest driver of third-party risk strategies at 37%, while regulatory compliance leads at 48%.
A 2026 retail and wholesale cyber-risk study also notes that digital partners now outnumber physical providers, increasing the potential systemic impact of a shared vendor vulnerability. Meanwhile, Kaspersky reported that 87% of retailers experienced cyber incidents during the previous 12 months, highlighting the broader security pressure facing retail technology environments.
Against this backdrop, POS vendor risk assessment and compliance consulting can help retailers evaluate whether POS providers can protect data, maintain reliable service, meet compliance requirements, and support uninterrupted store operations.
Why POS Vendor Risk Requires a Broader View
A POS vendor does more than provide transaction technology. The vendor may support payment processing, software, hardware, integrations, customer data, and store-level operations simultaneously. A cyber incident, system outage, compliance failure, or weak support process can therefore affect revenue and customer experience quickly. Retailers need to evaluate POS vendors across interconnected risks rather than relying only on onboarding checks or contractual assurances.
The Risk Factors that Matter the Most
A practical POS vendor review should focus on the factors most likely to affect transaction security and store continuity.
- Cybersecurity: Review security controls, vulnerability management, incident response, access controls, and data-protection practices to identify technology-related exposure.
- Reliability: Assess uptime, system performance, support responsiveness, recovery capabilities, and service-level adherence to understand operational dependability.
- Compliance: Examine PCI-related requirements, contractual obligations, privacy controls, certifications, and regulatory expectations to identify potential compliance gaps.
Together, these factors provide a clearer view of whether a POS provider is secure, reliable, compliant, and capable of supporting retail operations.
Nexdigm’s Role in Strengthening POS Vendor Risk Management
A POS vendor’s risk is rarely limited to the technology itself. Its impact can extend across payments, store operations, customer experience, data, and business continuity. Nexdigm looks at these connections to understand:
- How to Connect Technology With Operations: Consider how POS performance, integrations, and vendor support can influence transaction processing and day-to-day store activities.
- Business Exposure: Link vendor dependencies with transaction volumes, store coverage, customer impact, and the importance of uninterrupted POS availability.
- Focus on What Matters: Bring cybersecurity, reliability, compliance, and continuity indicators together to identify risks that deserve greater attention.
This broader lens helps retailers move from simply identifying POS vendor risks to understanding their potential business impact, creating a natural foundation for a deeper assessment.
From POS Risk Visibility to Structured Assessment
Understanding where POS vendor exposure exists is only the starting point. The next step is to determine how significant each risk is, what is driving it, and where action may be required. Nexdigm’s POS vendor risk assessment and compliance consulting approach can bring together vendor information, operational requirements, cybersecurity considerations, compliance indicators, and service performance to create a structured assessment.
This helps retailers move from a broad view of vendor exposure to a prioritized understanding of critical risks, providing a clear basis for remediation, enhanced monitoring, continuity planning, and vendor-management decisions.
Nexdigm’s POS Vendor Risk Assessment
Nexdigm’s POS vendor risk assessment and compliance consulting approach evaluates vendors across the areas most critical to secure and uninterrupted retail transactions. The assessment brings together the following areas to develop a structured view of exposure:
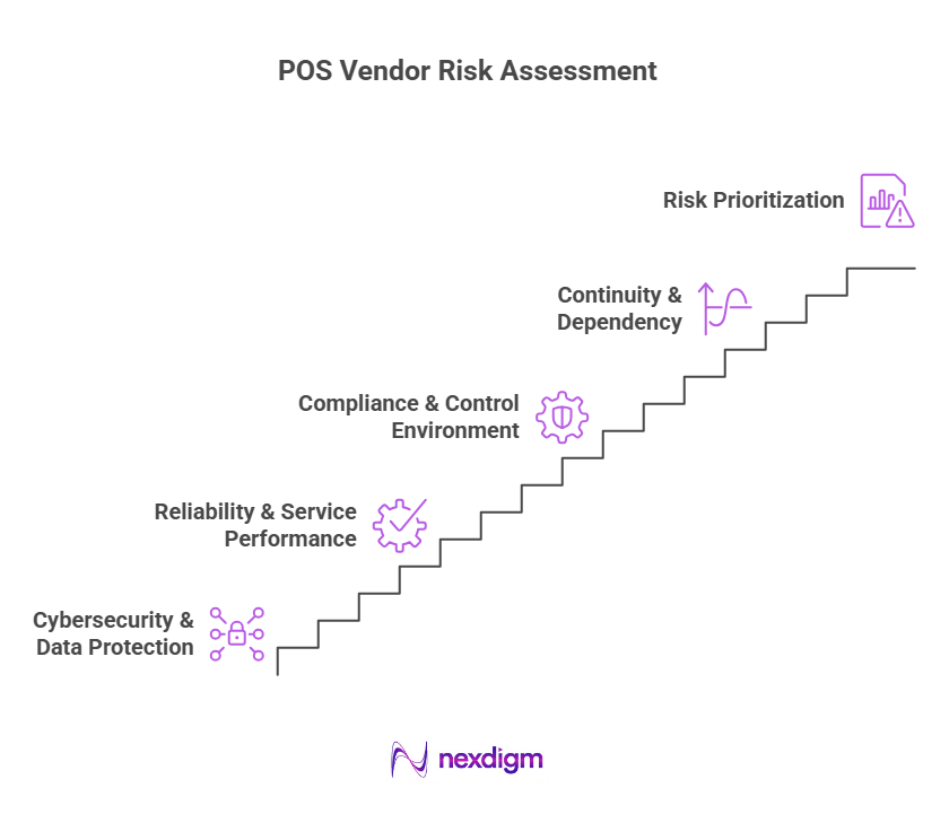
- Cybersecurity & Data Protection: Reviewing of security controls, access management, vulnerability practices, incident response, data handling, and relevant certifications to identify potential security exposure.
- Reliability & Service Performance: Examining uptime, incident history, response times, service-level adherence, technical support, and recovery capabilities to assess operational dependability.
- Compliance & Control Environment: Evaluation of applicable payment, privacy, contractual, regulatory, and internal requirements to identify documentation or control gaps requiring attention.
- Continuity & Dependency: Considering system dependencies, integrations, redundancy, recovery arrangements, vendor concentration, and alternative options to understand potential disruption exposure.
- Risk Prioritization: Assessing identified findings against vendor criticality, store coverage, transaction impact, and business importance to determine where remediation or enhanced monitoring should be prioritized.
The assessment gives retailers a clearer, risk-based view of POS vendors, helping them determine which relationships require attention and what actions can strengthen security, compliance, and service continuity.
Nexdigm’s Case
Nexdigm’s assessment identified 27% of POS vendors requiring enhanced risk monitoring, while 15% showed service-reliability concerns and 12% had compliance or documentation gaps. The review also identified 8% with elevated cybersecurity exposure and 6% with continuity-related vulnerabilities. Based on these findings, the retailer prioritized vendor remediation, stronger monitoring, contractual improvements, and continuity measures across its higher-risk POS relationships.
To take the next step, simply visit our Request a Consultation page and share your requirements with us.
Harsh Mittal
+91-8422857704